Continuous KYC refers to maintaining an informed view of customer identity and risk throughout the business relationship, rather than treating onboarding verification as permanently sufficient. It combines relevant change signals, periodic review and human assessment under a documented risk-based policy.
For teams researching continuous kyc, the most useful approach is to separate strategic objectives from the technical capabilities needed to deliver them. Financial institutions differ in business model, geography, data maturity and risk exposure, so a solution that performs well in one setting may fail in another. The practical guidance below focuses on operating decisions, measurable outcomes and questions that risk, compliance and technology teams can use together. Examples are illustrative rather than legal advice; local rules and regulated-entity obligations take precedence.
Why one-time onboarding has limits
A customer can change ownership, geographic reach, business activity or transaction behavior after verification. Screening data and adverse information may also change. A static record becomes less useful as those facts diverge from reality. Continuous KYC does not imply nonstop intrusive surveillance; it means defining meaningful triggers and keeping a defensible record of how the institution responds to material changes.
A useful workshop exercise is to write down the exact decision a reviewer must make, the source records supporting that decision and the evidence required to explain it months later. Where data is absent or contradictory, the process should show an exception rather than silently choosing the most convenient interpretation. This makes requirements testable and reduces misunderstandings between buyers, investigators and engineers.
Periodic versus event-driven reviews
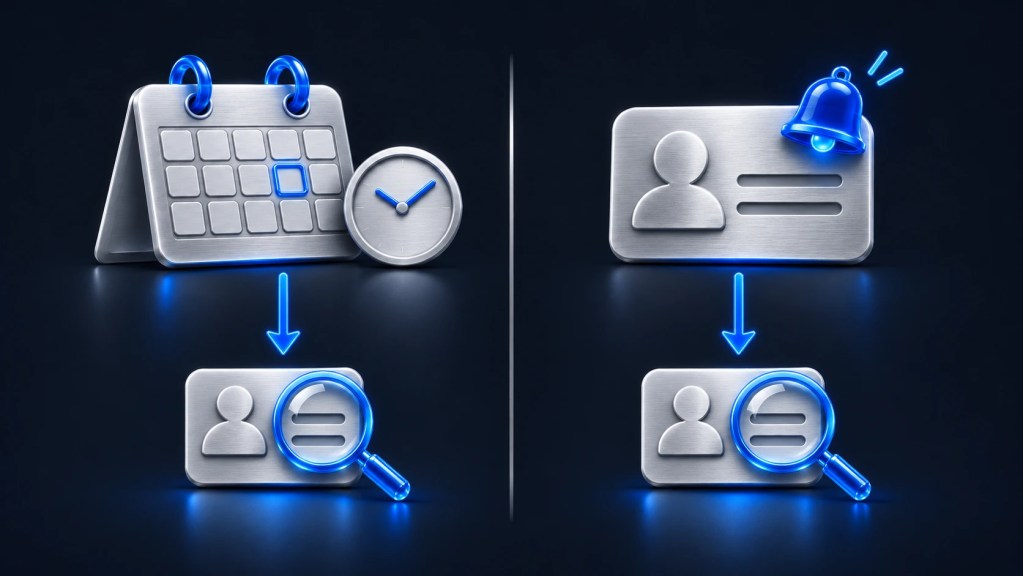
Periodic reviews occur at intervals set by policy and risk, while event-driven reviews respond to material changes. Both can be necessary. Events might include a new beneficial owner, significant activity deviation, higher-risk counterparties or a credible sanctions-screening update. Each trigger should lead to a proportionate action: no change, information request, enhanced due diligence, monitoring adjustment or escalation.
When assessing this capability, request a demonstration on an unfamiliar scenario instead of accepting a prepared success case. Ask who configures the thresholds or permissions, how a change is approved, what happens after failure and how an analyst verifies the conclusion. Capture the answer in written acceptance criteria that can be checked during implementation.
Building a useful trigger framework
Start by classifying triggers by reliability, urgency and potential impact. A confirmed ownership filing may justify a different response from an unverified news mention. Document who validates the signal, what evidence is required and how duplicates are handled. If third-party feeds are used, record coverage limits and update frequency. Without these controls, automated monitoring can generate repetitive tasks without improving risk understanding.
One operating risk is relying on a metric without its denominator or context. Teams should record the eligible population, the evaluation period and the method used to confirm outcomes. Comparing segments before and after deployment reveals shifts that blended averages can conceal. Any claimed improvement should have a reproducible method and a review owner.
Connect customer risk and transaction behavior
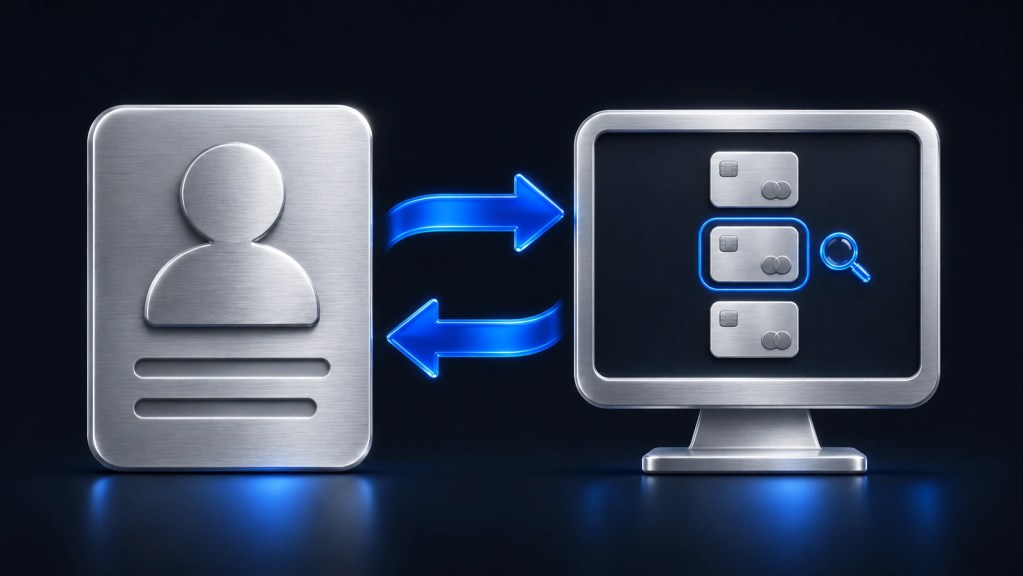
Expected activity models are only useful if refreshed when reliable evidence changes. Transaction anomalies can prompt review of a customer’s declared business purpose; an updated customer profile can in turn refine transaction monitoring. Avoid circular logic in which an unverified alert automatically raises the risk score and causes more alerts. Require an explicit evaluation before material changes to the customer risk tier.
For international deployments, identify what is uniform across the group and what must vary by local law, customer type or payment channel. Screening obligations, case disposition, retention and customer communication are not always interchangeable. A jurisdiction matrix linked to policies, configuration owners and escalation points can prevent global templates from obscuring local requirements.
Data and privacy foundations
Continuous review depends on reliable identifiers, permissions, data minimization and retention. Keep a clear lineage between source records, automated inferences and human conclusions. Role-based access matters when sensitive identity and financial data are involved. Assess cross-border transfers and vendor responsibilities before combining external watchlists, media sources and transaction histories.
A small controlled pilot is often more informative than a broad feature demonstration. Use a defined sample, known edge cases and a baseline process; include users responsible for investigations as well as technology. Record exceptions and remediation items, then decide whether the solution is ready to scale based on evidence rather than on the number of features shown.
Measure whether the process improves outcomes
Useful measures include overdue reviews by risk tier, time from material event to assessment, confirmed changes in customer risk, repeated false triggers, completeness of beneficial ownership records and investigator hours. A faster refresh process is not necessarily better unless decisions are consistent and substantiated. Audit samples should verify both that genuine changes are detected and that no unnecessary updates are imposed.
Documentation should survive changes in team members and vendors. Store the reason for configuration choices, source-system mappings, validation outcomes, access roles and relevant approvals. This reduces the risk that a technically functioning control becomes impossible to explain or reproduce during an internal review, independent audit or supervisory examination.
Using Formica AI in a continuous-risk strategy
Formica AI presents AML/KYC risk intelligence and transaction monitoring together in its broader platform messaging. Continuous KYC is a useful design lens for testing whether an institution can connect updated risk context with monitoring and investigation processes. Confirm available integration behavior and governance features before relying on the platform for specific compliance workflows.
The commercial decision should also reflect ongoing operating effort. Training, data-quality remediation, alert tuning, quality assurance and periodic control review all consume resources. Agree how performance will be measured after go-live, which teams will own follow-up and what events trigger an unscheduled review of configuration.
Practical checklist before deployment
- Define the specific risk scenarios and the decisions that the system must support.
- Verify data coverage, timeliness, quality controls and defensible entity matching.
- Test common legitimate behavior and difficult edge cases, not only known bad examples.
- Document thresholds, model versions, explanations, permissions and audit evidence.
- Measure detection outcomes together with customer experience and investigator workload.
- Confirm country-specific regulatory obligations with qualified compliance and legal teams.
- Assign clear owners for rollout, monitoring, review, incidents and continuous improvement.
Common implementation mistakes
Typical mistakes include selecting a provider on feature breadth alone; reusing static thresholds across customer segments; ignoring incomplete data; treating all alerts as confirmed wrongdoing; optimizing solely for fewer alerts; and deploying opaque models without a defensible explanation or rollback plan. Another frequent failure is separating procurement from frontline investigators, who ultimately know where a system creates or removes work. A buyer can avoid these problems by combining technical evaluation, risk governance and an evidence-based operational pilot.
Frequently asked questions
Is continuous KYC a separate law?
It is an operating approach; actual obligations arise from applicable customer due diligence and monitoring rules.
Does every event require full re-verification?
No. The response should be proportionate to the materiality and credibility of the event.
What is the difference between continuous KYC and transaction monitoring?
Continuous KYC manages evolving customer risk; transaction monitoring reviews activity. They should inform one another.
Conclusion
Continuous KYC should be approached as a practical risk and operating challenge, not as a search for a single perfect technology. Begin with clear use cases, select proportionate controls, test performance on representative evidence and preserve accountable oversight. A risk-based operating model should document the institution’s policies, local legal obligations, decision ownership and audit evidence. Technology should support these controls rather than be represented as a guarantee of legal compliance or elimination of financial crime.
Explore Formica AI
Explore Formica AI’s transaction monitoring capabilities and broader risk orchestration approach, or request a product discussion to evaluate fit against your workflows and data environment.
Transaction Monitoring: https://formica.ai/products/transaction-monitoring/
Formica AI Platform: https://formica.ai/