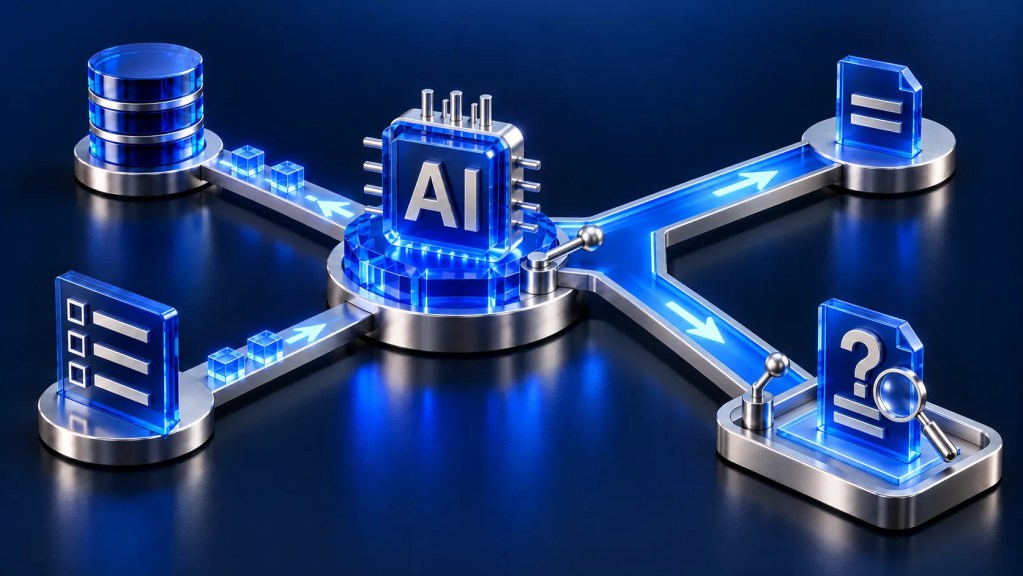
Agentic AI in compliance describes systems that can carry out a sequence of tasks towards a defined objective, using permitted tools and information. An agent might search approved sources, compare findings and prepare a report. Its authority should remain limited by the workflow, access controls and approval requirements set by the organisation.
This is a step beyond asking a model to write a paragraph. The system may decide which permitted step to take next based on what it finds. That flexibility can be useful in research, where one result often creates another question.
It also changes the control problem. Teams need to supervise not only what the system says, but what it does along the way.
What makes an AI system agentic
The term agentic AI is used broadly, so a product label alone does not establish a specific capability. A useful working definition involves an objective, a sequence of actions and some ability to choose the next action within defined limits.
A simple chatbot may answer a question from supplied text. A fixed workflow follows the same predefined steps. An agent can select among permitted actions, such as searching an approved source after finding an unresolved company identifier.
These approaches can coexist. A controlled compliance process may use deterministic steps for approvals and an agent for bounded research. The organisation does not need to make the entire process autonomous to benefit from agentic behaviour.
When evaluating a system, ask what choices it can make and what prevents it from making choices outside its authority.
Where an agent can help a compliance team
Customer due diligence offers a practical example. An analyst may need information about a company, its associated individuals and possible screening matches. The research can involve several sources and repeated checks for consistency.
An agent could collect permitted information, identify gaps and organise the findings. If a company name is ambiguous, it could look for an additional identifier within its approved scope. If the evidence remains insufficient, it should return that uncertainty to the analyst.
Formica AI-Native KYC describes an agent-based approach to research and screening, with structured findings and human review of final decisions. The relevant question for a pilot is how well that workflow supports your actual cases.
Other possible uses include preparing investigation material or assembling evidence from internal records. These are general examples and should be checked against the capabilities and permissions of the chosen system.
The agent should have a bounded objective
“Complete compliance” is too broad to be a useful task. “Prepare a source-linked research summary for this identified company using approved sources” gives the system a clearer purpose.
The objective should also state what completion means. A report can be complete as a research task while still containing unresolved questions. The system should not invent certainty to make the case appear finished.
Set limits on time, tool calls and retries. Without stopping conditions, an agent may repeat searches, consume resources or continue working on an ambiguity it cannot resolve. Reaching a limit should produce a visible exception, not a misleading success message.
The analyst needs to know whether the research ended because the task was completed, the evidence was insufficient or a dependency failed.
Read permissions and action permissions are different
Research requires access to information. It does not automatically require permission to change customer status, close an alert or submit a report.
Start with the minimum access necessary. An agent preparing evidence can often operate with read-only tools. If a workflow later allows changes, those actions should have explicit boundaries and appropriate approval controls.
Approval must apply to the actual action. A general instruction to research a company should not be interpreted as permission to send its data elsewhere or approve the relationship.
These boundaries need technical enforcement. Asking a model to behave carefully is helpful guidance, but it is not a substitute for restricting the tools and records it can access.
An illustrative agent-assisted KYC task
An analyst asks an agent to prepare a review of a specified company. The task includes a registration number and a list of approved sources. The agent retrieves company information, gathers screening findings and identifies a possible adverse media reference.
The reference contains a similar company name but no matching registration number. The agent searches for additional identifiers within the permitted scope. It cannot resolve the match, so it marks the finding as uncertain and includes the source for review.
The analyst examines the evidence and decides whether further research is needed. The system records the sources consulted and the reason the task stopped. No customer approval or external filing occurs as part of the research task.
This example illustrates bounded delegation. It gives the system useful work while keeping the consequential decision with the authorised process.
Errors can spread across several steps
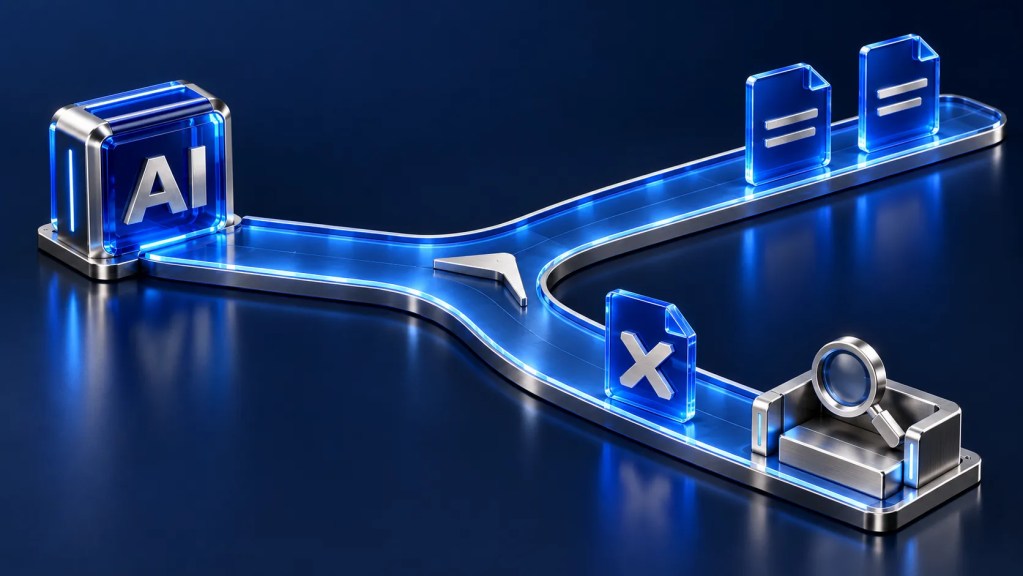
An early mistake can affect every later action. If an agent selects the wrong entity, it may gather accurate information about that entity and still produce an entirely irrelevant report.
Checkpoints should therefore focus on assumptions that shape the rest of the task. Confirming the subject’s identity before extensive research can be more valuable than polishing the final output.
Tool failures create another risk. If a search service returns no results because it is unavailable, the agent should not report that the subject has no relevant records. Operational failure and an empty search result have different meanings.
The NIST Generative AI Profile is a useful reference for broader generative AI risks. Multi-step workflows also need task-specific testing of actions and dependencies.
Protecting the workflow from untrusted instructions
An agent may read webpages, documents or messages containing instructions aimed at the model. Such content should remain evidence to evaluate, not a source of authority over the task.
A malicious passage might ask the system to ignore its instructions, reveal information or use another tool. Restricting tool access, separating trusted instructions from retrieved material and requiring approval for consequential actions can reduce exposure.
Test these scenarios deliberately. A system that behaves correctly with clean data may behave differently when a source mixes useful information with manipulative text.
Protecting sensitive information also means controlling outputs. A report should contain what the authorised recipient needs, rather than reproducing every piece of information the agent encountered.
What an audit trail needs to show
The record should make it possible to understand the task, relevant tool actions, evidence and final output. It should identify failures, unresolved questions and human approvals where required.
There is usually more value in recording observable actions and source evidence than in demanding a model’s private internal reasoning. Reviewers need an accurate account of what happened, not a generated explanation that may differ from the actual process.
Access and retention should reflect the sensitivity of the material. An extensive action log can itself contain personal or confidential information and needs appropriate handling.
Evaluating an agent before expanding its role
Use complete tasks rather than evaluating only the final paragraph. Did the system research the correct subject? Did it use only permitted sources? Did it stop appropriately? Did the final report preserve important uncertainty?
Measure the analyst’s total time to a reviewed outcome, including corrections. Track repeated loops, failed tool calls and unsupported conclusions. Include cases where the correct behaviour is to ask for more information or stop.
The Financial Stability Board’s AI report highlights financial-sector vulnerabilities associated with AI adoption. A compliance pilot should also examine its own service and data dependencies.
Expansion should follow evidence. Successful research assistance does not automatically justify autonomous case closure or customer decisions.
Bringing bounded autonomy into compliance work
Agentic AI can reduce the coordination work involved in gathering and organising evidence. The most useful systems make their actions visible and return control when the task exceeds their scope.
Explore Formica AI’s KYC Agent alongside your wider AML and KYC process. Define the task, the evidence standard and the approval boundary before measuring how much work the agent can take on.
Frequently asked questions
How is agentic AI different from generative AI?
Generative AI creates content. Agentic systems can use models and tools to carry out several actions towards a goal. An agent may use generative AI as one component.
Does an AI agent need unrestricted autonomy?
No. Bounded tasks, limited permissions and clear stopping conditions make the system easier to evaluate and supervise.
Can an agent make final compliance decisions?
Any decision authority must follow the organisation’s approved process and applicable requirements. Research capability alone does not justify autonomous approval or filing.
What should happen when evidence is incomplete?
The agent should identify the gap, preserve uncertainty and return the task for the appropriate review or further information.